 TL;DR:
False positive deletion happens when security programs mistakenly identify and eliminate safe files as malware, meaning you should always verify the file with a reputable scanner before attempting to restore it from quarantine or backups.
● Stop using the affected storage immediately and never install recovery software or save restored files directly onto the original drive to avoid overwriting the missing data.
● Data recovery tools like Wondershare Recoverit can retrieve surviving local files but will not neutralize active security threats, bypass encryption, or fix physically damaged drives that are clicking or overheating.
● Built-in version histories and recent backups are the safest recovery methods, as securely erased or fully overwritten files generally cannot be reconstructed by standard software.
Ask AI for a summary
 ChatGPT
 Perplexity
 Gemini
 Claude
 Grok
false positive deletion refers to legitimate file mistakenly removed after incorrect malware detection This guide explains how it works, where problems arise, and which recovery steps preserve the best chance of retaining important information.
Try Recoverit to Perform Data Recovery
 Security Verified. 3,591,664 people have downloaded it.
In this article
What Is false positive deletion
false positive deletion is associated with legitimate file mistakenly removed after incorrect malware detection The term matters because a file that is unavailable is not always deleted: it may be encrypted, cloud-only, damaged, or simply hidden by an application.
Identify the underlying device, service, file format, and available backups before choosing a repair or recovery tool. A safe first step is to keep an unchanged copy of any accessible original.
How Does false positive deletion Work
Legitimate file mistakenly removed after incorrect malware detection In practice, the operating system or application interprets the relevant data and exposes it to the user. Problems may occur when credentials, metadata, storage media, or software compatibility change.
Confirm the file is safe with reputable scanning before restoring from quarantine or backup. This distinction helps separate normal behavior from genuine data loss and prevents unnecessary formatting, overwriting, or repeated repair attempts.
Types and Common Scenarios for false positive deletion
Typical Uses and Examples
For false positive deletion, a common scenario is routine access to a stored file, device, or account. Legitimate file mistakenly removed after incorrect malware detection A second scenario involves a missing or inaccessible item, where the best next step depends on whether the original bytes still exist.
Limitations and Recovery Boundaries
Malware removal and incident response require security tools; file recovery does not neutralize threats. Backups and built-in version histories are often preferable to scanning. Overwritten or securely erased data generally cannot be reconstructed by ordinary recovery software.
Practical Tips for false positive deletion
- Confirm the file is safe with reputable scanning before restoring from quarantine or backup.
- Check recent backups, previous versions, and built-in restore options before changing the source.
- Record error messages, file locations, and account or device details for diagnosis.
- Do not install recovery software or save recovered files onto the affected storage.
- Use a verified copy for risky tests, updates, or repairs whenever possible.
- For failing hardware or critical evidence, stop repeated attempts and contact a specialist.
When working with false positive deletion, prioritize preserving the original and verifying restored copies before removing backups or resuming normal use.
How to Use Recoverit to Recover Lost Data
If false positive deletion involves a missing local file on a supported, accessible computer or removable drive, Wondershare Recoverit may help scan that storage. Check the Recoverit official website for supported devices and formats. Malware removal and incident response require security tools; file recovery does not neutralize threats. Recoverit does not replace account recovery, password retrieval, malware removal, or specialist hardware repair.
Key Features Offered by Recoverit
- Scan supported local drives for recoverable file records and recognizable content.
- Inspect available scan results and use deeper scanning when appropriate.
- Preview supported file types and export selected results to a separate healthy destination.
Step-by-Step Guide on How To Recover Lost Data
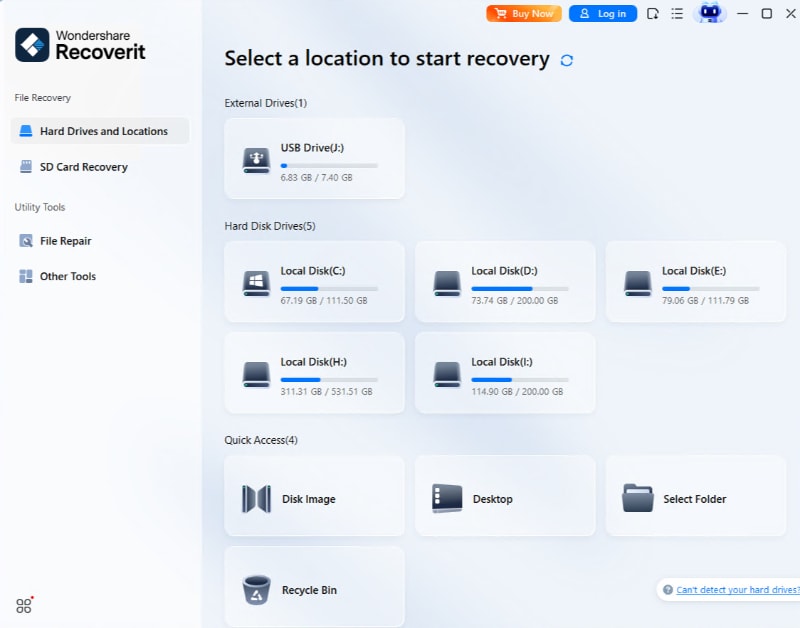
1. Choose a Location to Recover Data
Launch Recoverit and select the supported local drive where a missing file was previously stored. Do not scan a device that is clicking, overheating, repeatedly disconnecting, or physically damaged.
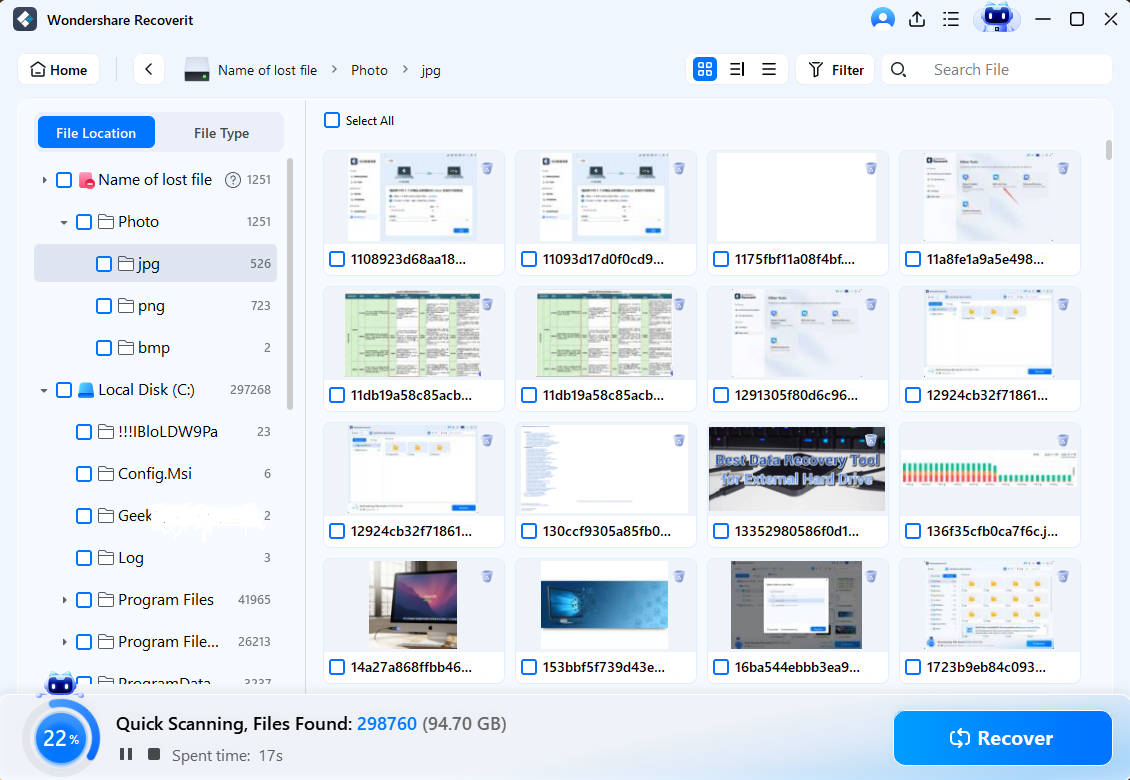
2. Deep Scan the Location
Allow the scan to finish without writing new data to the affected drive. Results depend on surviving readable data; a cloud-only item, locked encrypted volume, or compromised operating system may require another workflow.
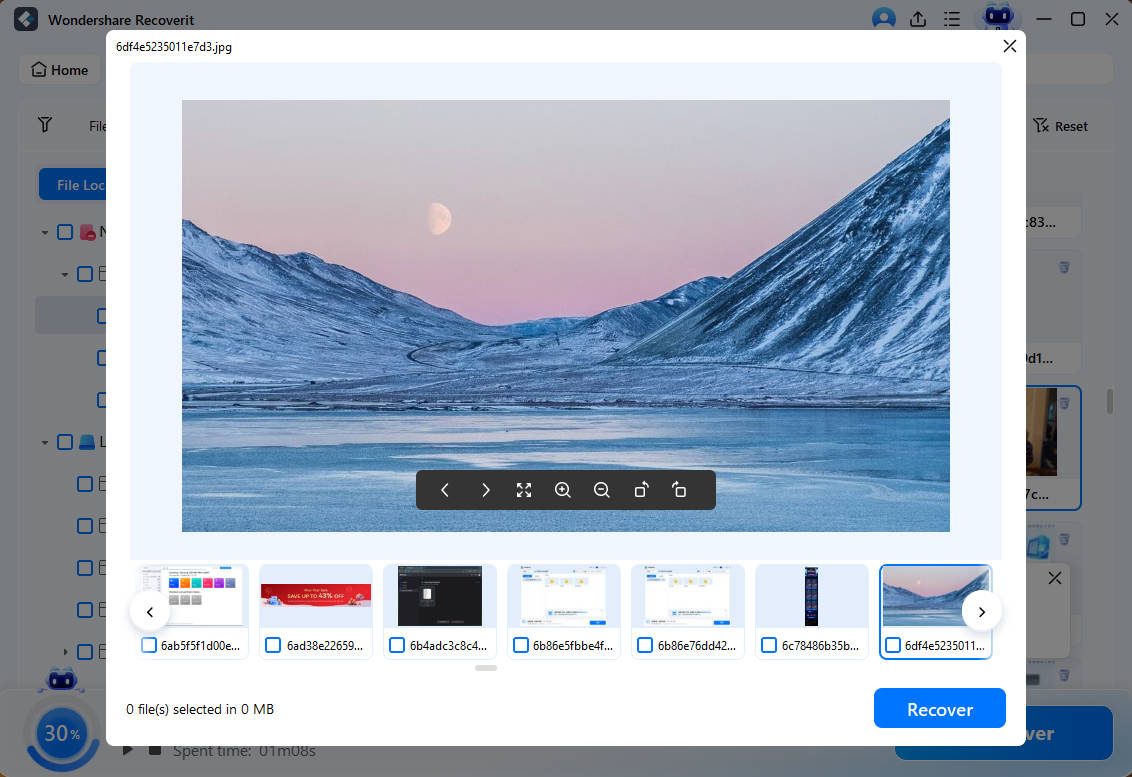
3. Preview and Recover Your Desired Data
Preview supported results, choose the relevant files, and save them to a different healthy drive. Verify that the exported copies open correctly before changing the original storage.
Conclusion
false positive deletion is best understood in the context of its actual storage and access mechanism. Confirm the file is safe with reputable scanning before restoring from quarantine or backup. Preserve original data, use native restore options first, and choose local recovery software only when the device and files are suitable for scanning.
Next: Bitlocker
FAQ
What does false positive deletion mean?
Legitimate file mistakenly removed after incorrect malware detectionWhat is the safest first step for false positive deletion?
Confirm the file is safe with reputable scanning before restoring from quarantine or backup. Preserve the original and check available backups before changing files or settings.Can Recoverit fix every false positive deletion problem?
No. Recoverit may recover surviving local files on supported storage, but it cannot bypass encryption, restore cloud-only records directly, eliminate malware, or repair failed hardware. Malware removal and incident response require security tools; file recovery does not neutralize threats.


